SAP Cloud Platform Integration, now part of SAP Integration Suite, provides integration capabilities for connecting SAP and non-SAP applications across cloud, on-premise, and hybrid environments. Security and authentication are essential because integration flows can exchange business data between systems such as SAP S/4HANA, SAP SuccessFactors, SAP Ariba, Salesforce, databases, APIs, and external services.
A secure integration architecture controls who can access an integration service, which systems can communicate, how messages are authenticated, and how sensitive information is protected.
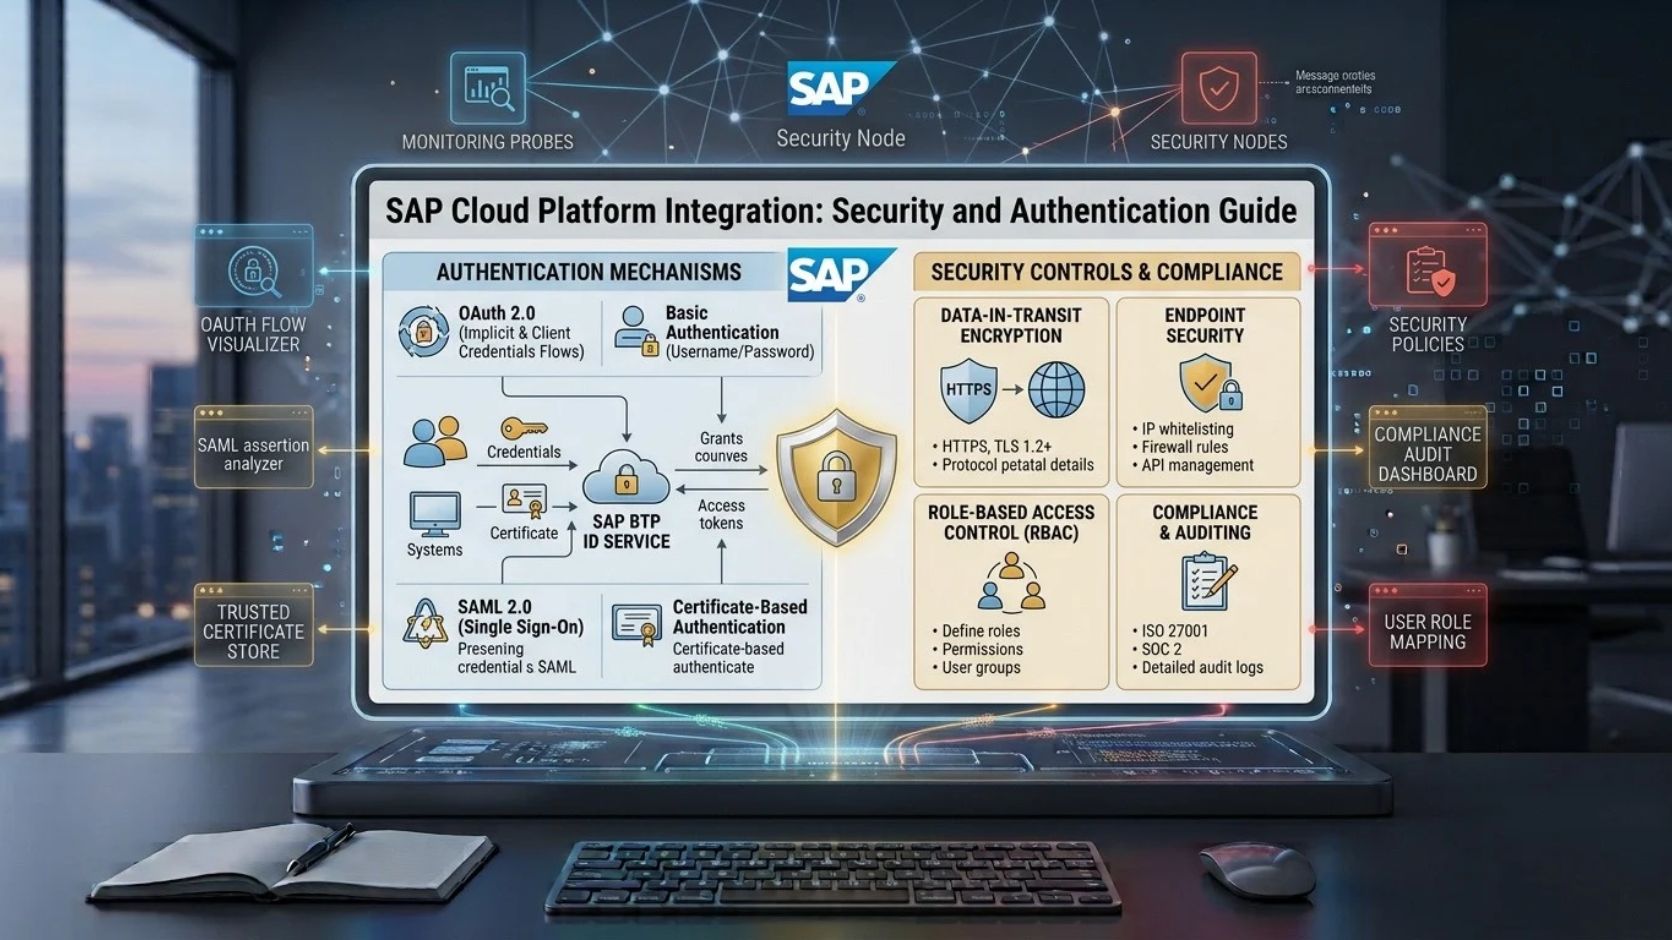
SAP Cloud Integration supports several authentication and security mechanisms. These can include OAuth 2.0, client certificates, basic authentication, SSH keys, and other supported security configurations, depending on the integration scenario and adapter.
Destinations can also be used in relevant SAP environments to manage connection information for applications and services. A destination may contain endpoint information, authentication configuration, and other connection properties.
What Is Security in SAP Cloud Platform Integration?
Security in SAP Cloud Platform Integration covers the controls used to protect integration flows, APIs, credentials, messages, endpoints, and connected applications.
An integration platform can act as a central communication layer between many systems. This makes security important at multiple points.
For example:
S/4HANA → Cloud Integration → Salesforce
In this architecture, Cloud Integration must securely communicate with both the sender and receiver. The integration flow may also transform business information before sending it to the target application.
Security therefore includes authentication, authorization, encryption, credential management, certificate management, network protection, and secure monitoring.
Why Security and Authentication Matter
Enterprise integration can involve sensitive business information such as customer records, financial transactions, employee data, supplier information, sales orders, invoices, and inventory details.
Unauthorized access could expose or modify this information.
Authentication confirms the identity of a user, system, or application. Authorization determines what that authenticated identity is allowed to access.
These two concepts are different.
For example, an application may successfully authenticate with an API but still receive a 403 Forbidden response because it does not have permission to access a particular resource.
A secure integration design must therefore address both authentication and authorization.
Authentication vs Authorization
Authentication answers the question:
“Who or what is requesting access?”
Authorization answers:
“What is that identity allowed to access?”
An application may use OAuth 2.0 to authenticate against an API. The API can then use scopes or other access controls to determine which resources the application can use.
Similarly, an S/4HANA integration may require a technical user or another supported identity with specific permissions.
Using authentication without appropriate authorization controls does not provide complete access protection.
Common Authentication Methods in SAP Cloud Integration
The appropriate authentication method depends on the connected system, adapter, interface, security requirements, and SAP architecture.
Common methods include:
OAuth 2.0: Used for token-based authorization and access to supported APIs and services.
Basic Authentication: Uses a username and password. It is generally used only where the target service supports it and where secure transport is configured.
Client Certificate Authentication: Uses digital certificates to establish trust between systems.
SSH Authentication: Commonly used for secure file transfer scenarios such as SFTP, often using SSH keys.
The selected method should match the security capabilities of the target application.
OAuth 2.0 in SAP Cloud Integration
OAuth 2.0 is a widely used authorization framework for API-based communication.
Instead of sending a username and password with every API request, an application can obtain an access token from an authorization server and use that token to access protected resources.
A simplified process is:
Client → Authorization Server → Access Token → API
The token provides the access required by the API according to the configured authorization rules.
OAuth 2.0 configurations can involve client IDs, client secrets, scopes, token endpoints, and access tokens. Exact requirements depend on the service provider.
Access tokens should be treated as sensitive security information and should not be exposed unnecessarily in logs or message payloads.
Basic Authentication
Basic Authentication sends a username and password as part of an HTTP authentication mechanism.
When used over HTTPS, the communication channel is encrypted during transmission. However, Basic Authentication still requires careful credential management.
Passwords should not be placed directly inside integration-flow logic or exposed through logs.
Where a stronger authentication mechanism is supported and required by the target system, organizations may use alternatives such as OAuth 2.0 or certificate-based authentication.
Client Certificate Authentication
Client certificates can provide certificate-based authentication between communicating systems.
A certificate identifies the client and participates in establishing a trusted secure connection.
Certificate-based authentication is commonly used when strong machine-to-machine authentication is required.
Certificate management includes key generation, certificate installation, trust configuration, expiration monitoring, and renewal.
An expired certificate can cause an integration to fail even when the integration flow itself has not changed.
SFTP and SSH Authentication
File-based integrations frequently use SFTP, which operates through SSH.
An SFTP connection can use username/password authentication or SSH key-based authentication depending on the server and integration configuration.
SSH keys are commonly used for automated system-to-system file transfer because they avoid the need to store a traditional password for every automated connection.
The private key must be protected carefully. It should not be exposed in source code, logs, or message content.
HTTPS and Transport Encryption
HTTPS uses TLS to protect data while it travels between systems.
Encryption helps prevent unauthorized parties from reading or modifying data during network transmission.
For API and HTTP-based integrations, HTTPS should be used when supported and required by the security architecture.
TLS configuration can also involve server certificates and trust relationships.
A certificate problem may cause connection failures when the client cannot establish trust with the server.
Trust Configuration and Certificates
Certificates are an important component of secure enterprise integration.
A certificate can establish trust between the integration platform and a remote server or client.
Certificate-related problems may occur when:
- A certificate has expired.
- A certificate is not trusted.
- The certificate chain is incomplete.
- The hostname does not match the certificate.
- A required client certificate is missing.
- The wrong certificate is configured.
Certificate validity should be monitored before expiration to reduce unexpected integration failures.
Destinations and Authentication
Destinations provide connection information for accessing services and applications in supported SAP environments.
A destination can contain information such as the target URL, authentication type, and connection properties.
For example, an application may use a destination to identify an S/4HANA API endpoint without embedding the endpoint and authentication configuration directly into application code.
This separation can make connection management easier when environments change.
Development, testing, and production environments often use different endpoints. The appropriate destination configuration must therefore point to the correct environment.
Secure Management of Destinations
Destinations should be configured according to the security requirements of the connected application.
Sensitive information should not be exposed unnecessarily. Access to destination configuration should be limited to authorized users and services.
When a destination uses credentials, certificates, or OAuth-related information, the security of those credentials becomes part of the overall integration security architecture.
A change to a destination can affect every application or integration flow that depends on it. Changes should therefore be controlled and tested.
Authorization in SAP Cloud Integration
Authorization determines what a user or technical identity can do after authentication.
Cloud Integration environments can use role-based access controls to restrict administrative and development functions.
Different users may need different permissions. A developer may require integration-flow development access, while an operations user may primarily need monitoring access.
Applying appropriate roles reduces unnecessary access to integration artifacts and runtime information.
The exact roles and permissions depend on the SAP BTP environment, subscription, services, and configured security architecture.
Role-Based Access Control
Role-based access control assigns permissions based on defined roles.
For example, access to development functions can be separated from operational monitoring functions.
This supports the principle of least privilege, where users and technical identities receive only the permissions required for their tasks.
Administrative access should be limited because administrative functions can affect integration flows, security settings, credentials, and runtime behavior.
Secure Credential Management
Credentials are one of the most important security elements in an integration environment.
Passwords, client secrets, private keys, tokens, and certificates should be managed through appropriate secure mechanisms.
Credentials should not be hard-coded into scripts or integration messages.
When credentials need to be rotated, the related configuration should be updated without exposing the new credential to unauthorized users.
Credential rotation is particularly important for long-running enterprise integrations.
API Security
API-based integration requires protection at the API layer as well as the integration platform.
API security can involve authentication, authorization, rate controls, input validation, TLS encryption, and monitoring.
For example, an S/4HANA API may require OAuth-based access and specific permissions.
Cloud Integration can act as an intermediary that receives a message, validates or transforms the data, and calls the target API.
API credentials and tokens should not be written to logs or exposed through error responses.
Security for SAP S/4HANA Integration
S/4HANA integration may involve OData, REST, SOAP, IDoc, and other interfaces.
Each interface can have different security requirements.
For example, an OData service may use HTTPS and an authentication mechanism supported by the S/4HANA environment. An IDoc scenario may require a different technical configuration.
For on-premise S/4HANA systems, secure connectivity between the internal network and cloud services must also be considered.
A hybrid architecture can look like:
S/4HANA On-Premise → Secure Connectivity → Cloud Integration → External Application
Security must be maintained across each connection in this architecture.
Security for Cloud-to-Cloud Integration
Cloud-to-cloud integrations connect services that operate outside a traditional internal network.
For example:
S/4HANA Cloud → Cloud Integration → Salesforce
Each application may use its own identity provider, API authentication method, certificates, or authorization model.
Cloud Integration must therefore be configured to meet the requirements of both systems.
Using HTTPS, OAuth 2.0, certificates, secure credentials, and appropriate authorization can help protect the communication path.
Security for Hybrid Integration
Hybrid integration connects cloud applications with on-premise systems.
Security considerations include network connectivity, authentication, certificates, firewall rules, identity management, and authorization.
A secure connectivity component may be used to establish communication between cloud services and internal applications.
The architecture should prevent unauthorized external access to internal systems while allowing required business communication.
Data Protection in Integration Flows
Integration flows can process large amounts of business information.
Data protection should consider what information is collected, transformed, transmitted, logged, and stored during processing.
Sensitive information should only be processed when required for the business process.
Message logging should be controlled carefully. Full message payload logging may expose customer data, financial information, personal information, or other confidential content.
Where detailed logging is required for troubleshooting, organizations should apply appropriate data protection and access controls.
Security Risks in Integration
Common integration security risks include exposed credentials, weak authentication, excessive permissions, unsecured endpoints, expired certificates, insufficient logging controls, and unauthorized access to integration artifacts.
Hard-coded passwords are particularly risky because they can remain inside source files or configuration artifacts.
Another risk is giving a technical user more permissions than required.
Security reviews should therefore examine both the integration platform and every connected system.
Security Monitoring and Error Handling
Security monitoring is closely connected to operational monitoring.
A failed authentication attempt can indicate an incorrect configuration, an expired credential, or an unauthorized access attempt.
For example, repeated 401 Unauthorized responses may indicate authentication problems. Repeated 403 Forbidden responses may indicate authorization problems.
Integration teams should distinguish between normal configuration errors and suspicious access patterns.
Error messages should also avoid exposing passwords, tokens, private keys, or other sensitive security information.
Secure Integration Development
Security should be considered during integration design and development.
Integration developers should select appropriate authentication mechanisms, protect credentials, validate incoming data, avoid unnecessary logging, and apply suitable authorization controls.
Testing should include successful authentication as well as invalid credentials, expired certificates, missing permissions, invalid tokens, and unauthorized requests.
Security testing should also verify that error messages do not expose confidential information.
Security Testing Before Production
Before deploying an integration flow to production, security-related scenarios should be tested.
For example, testing can verify that an invalid credential is rejected, an unauthorized user cannot access restricted resources, and an expired certificate produces an identifiable error.
API access should be tested with valid and invalid tokens where the testing environment supports it.
Destination configurations should also be verified to ensure that the correct endpoint, authentication method, and environment are being used.
Testing should not rely only on successful business transactions. Failure scenarios are also important.
Security Best Practices for SAP Cloud Integration
A secure implementation should use supported authentication mechanisms, encrypted transport, controlled access, and secure credential management.
Permissions should be limited according to job responsibilities. Integration flows should not contain hard-coded passwords or private security information.
Certificates and credentials should have defined renewal and rotation processes.
Destinations should be reviewed when endpoints, credentials, certificates, or authentication mechanisms change.
Logs should contain enough information for troubleshooting without exposing unnecessary sensitive data.
Security configuration should also be reviewed when integrations are moved between development, test, and production environments.
Frequently Asked Questions
What is SAP Cloud Platform Integration security?
SAP Cloud Platform Integration security includes authentication, authorization, encryption, certificate management, credential protection, secure connectivity, access control, and monitoring.
What authentication methods does SAP Cloud Integration support?
Depending on the integration scenario, supported authentication mechanisms can include OAuth 2.0, Basic Authentication, client certificates, SSH authentication, and other adapter-specific methods.
What is OAuth 2.0 used for in SAP Cloud Integration?
OAuth 2.0 is used for token-based authorization when accessing supported protected APIs and services. It allows applications to use access tokens instead of sending a username and password with every request.
What are Destinations in SAP integration?
Destinations provide connection information for applications and services in supported SAP environments. They can contain information such as a target URL, authentication configuration, and connection properties.
Can Destinations contain authentication information?
Yes. Depending on the destination type and configuration, authentication-related information can be associated with a destination. Sensitive credentials should always be protected through the supported security mechanisms.
How does SAP Cloud Integration protect data during transmission?
HTTPS and TLS can encrypt data during network transmission. Other secure protocols, such as SFTP over SSH, can provide encrypted communication for file-based integrations.
What is the difference between authentication and authorization?
Authentication verifies an identity. Authorization determines what that identity is permitted to access or perform.
How are certificates used in SAP Cloud Integration?
Certificates can establish trust and support secure authentication between systems. They can be used for server trust and, where configured, client certificate authentication.
How can S/4HANA be securely connected to Cloud Integration?
The appropriate architecture depends on whether S/4HANA is cloud or on-premise. Secure APIs, HTTPS, authentication mechanisms, certificates, and secure connectivity components can be used according to the deployment and interface requirements.
Why is secure credential management important?
Credentials such as passwords, client secrets, tokens, and private keys provide access to systems and services. If they are exposed, unauthorized parties may gain access to protected resources.
Conclusion
SAP Cloud Platform Integration security requires protection across the complete integration lifecycle. Authentication establishes the identity of users and systems, while authorization controls the resources they can access.
OAuth 2.0, certificates, HTTPS, SFTP, SSH, Basic Authentication, role-based access, and secure credential management can be used according to the integration scenario. Security requirements vary between S/4HANA, SAP applications, third-party platforms, APIs, and on-premise systems.
Destinations can support secure connection management in relevant SAP environments by providing endpoint and authentication configuration. Correct destination configuration is particularly important when integrations use different development, testing, and production environments.
A secure Cloud Integration architecture also requires controlled access, protected credentials, certificate management, appropriate logging, secure APIs, and regular security testing. These controls help protect business data while maintaining reliable communication between SAP and external applications.